Looking for the latest information on 60 Fflush Stream Function In C? We've researched comprehensive data, records, and insights about 60 Fflush Stream Function In C.
Main Features
Explore the main sources for 60 Fflush Stream Function In C.
Recent Updates
Stay updated on 60 Fflush Stream Function In C's latest milestones.
Use of fflush(stdin) function in C||Character skipping problem of scanf()||C programming Tutorial
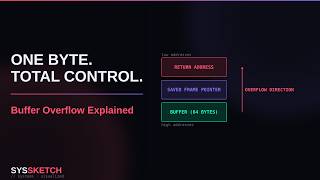
Buffer Overflow Explained: How One Byte Hijacks a Program
Why do we need to flush the input buffer in C
fflush
Why We Should Never Use gets()... And Why To Use fgets() Instead | C Programming Tutorial
How to Use fdopen() and setvbuf() to Change Buffering Without Affecting stdout
Resolving FLASH Overflow on STM32C031C6 During FFT with ARM CMSIS-DSP
How to create functions with a variable number of arguments using stdarg.h | C Programming Tutorial
How To Clear The Input Buffer | C++ Tutorial
Understanding the putchar() Mechanism and Input Buffering in C
why do hackers love strings
Expert Insights
Data is compiled from public records and verified media reports.
Last Updated: October 1, 2026
Conclusion
For 2026, 60 Fflush Stream Function In C remains one of the most talked-about information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
This video is an effort towards explaining the working of output buffers, flush(), and why How to clear the standard input buffer in An overview of how to use the memset() In this video, we're gonna talk about A buffer is just a fixed-size block of memory — and the moment a program writes past its edge, the extra bytes don't vanish, they ... Why we should never use the gets() Learn why FLASH overflow occurs on STM32C031C6 when implementing FFT with ARM CMSIS-DSP and how to choose the ... How to clear the input buffer in Hackers have been trying to steal information since the beginning of the information age. Buffer overflow attacks have been one of ...