Looking for the latest information on Aquiring A Memory Image Using Dumpit? We've researched comprehensive data, records, and insights about Aquiring A Memory Image Using Dumpit.
Core Information
Explore the primary sources for Aquiring A Memory Image Using Dumpit.
Developments
Stay updated on Aquiring A Memory Image Using Dumpit's latest milestones.
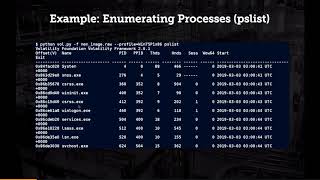
How to use Volatility - Memory Analysis For Beginners.
Installing and Using FTK Imager, Capturing the Volatile Memory, RAM DUMP, DumpIt, Belkasoft Memory
Memory Forensics with Volatility and Dumpit - Cyber Secrets S01E10
Rapid Windows Memory Analysis with Volatility 3
How to Capture Memory Dump (Magnet Forensics way)
How to Analyze Malware Using Volatility Tool and DumpIt Tool | Memory Forensics | Malware Analysis
Memory Forensics Using the Volatility Framework
Memory Forensics with ProcessHacker & DumpIt
Use of Dumpit as a Digital Forensic Tool for Memory Forensic
Capturing Windows Memory (RAM) Dump with DumpIt
Digital Forensics with DumpIt - Memory Acquisition Made Simple
Expert Insights
Data is compiled from public records and verified media reports.
Last Updated: September 28, 2026
Conclusion
For 2026, Aquiring A Memory Image Using Dumpit remains one of the most searched-for information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
This is a short tutorial to show you how to " This presentation mainly focuses on the practical concept of Okay okay now it is not giving any error and see this is creating a r aw jh.live/cysec || Find your next cybersecurity career! CySec Careers is the premiere platform designed to connect candidates ...