Looking for the latest information on Decoding Packets In Wireshark? We've compiled comprehensive data, records, and insights about Decoding Packets In Wireshark.
Key Details
Explore the primary sources for Decoding Packets In Wireshark.
History
Stay updated on Decoding Packets In Wireshark's newest achievements.
Using Wireshark's Decode As Feature
Wireshark Decode as
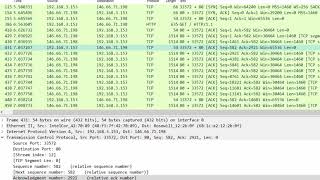
Observing a TCP conversation in Wireshark
Decoding Packets in Wireshark
Wireshark Decode As Example
How To Capture Packets From Any Website Using Wireshark (TCP/UDP/IP, etc.)
Packet Class: Wireshark - Lua Protocol Dissectors
How to capture ethernet packets in Wireshark
CTF for beginners: Using wireshark to sniff secrets and then decode them with a Key
Decoding Modbus RTU Captures in Wireshark
Decrypting HTTPS Traffic With Wireshark
Deep Dive
Data is compiled from public records and verified media reports.
Last Updated: September 29, 2026
Final Thoughts
For 2026, Decoding Packets In Wireshark remains one of the most talked-about information profiles. Check back for the latest updates.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
In this live event I will be playing with In this tutorial, we are going to capture the client side session keys by setting an environment variable in Windows, then feed them ... In this video we will learn about how to There are many scenarios when you work on a trace file and your protocol analyzer doesn't I'm giving an idea of what you can expect in my " This is from AccessDenied CTF 2022 and its called Shark1. In this challenge we have a pcap file (which is a captured network ... In this video, I cover the process of decrypting HTTPS traffic with